


Latest from Alex
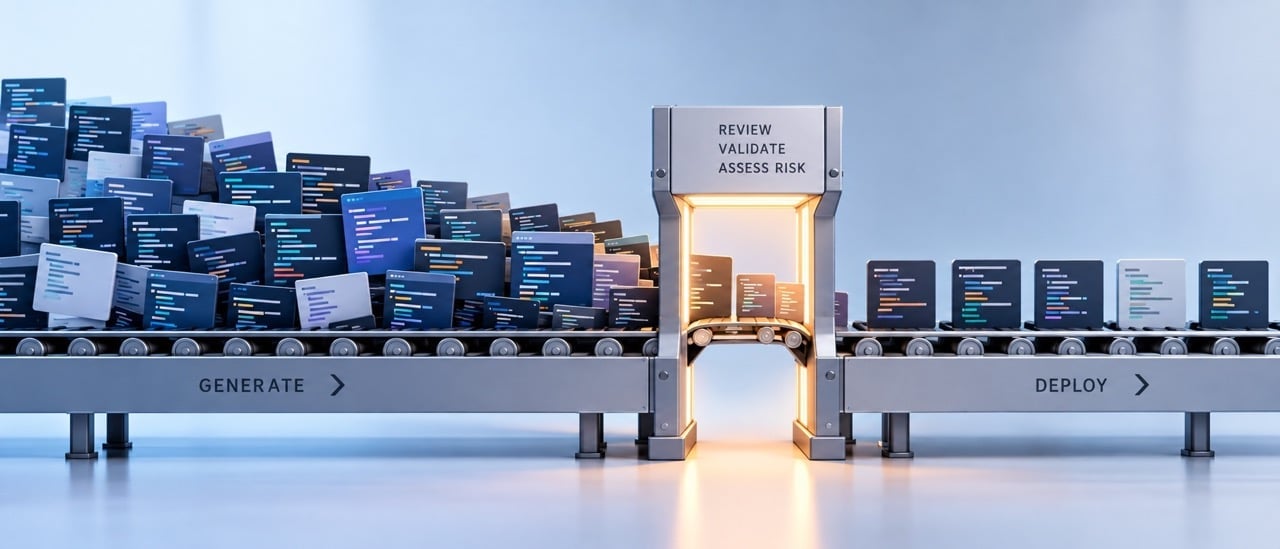
Test Creation Was Never the Bottleneck
Something specific happened to software delivery in the past two years. The 2026 survey data is unusually clear about what it was. Sonar’s 2026 State of Code Developer Survey found that AI-generated or AI-assisted code accounted for 42% of code committed by respondents, with developers projecting that share to reach 65% by 2027. GitLab’s 2026 […]
Sep 9, 2026 · 3 minAll articles by Alex Vakulov
Showing 1–7DevOps Is Drowning in Updates—and Engineering Is Paying the Price
DevOps used to be a manageable rhythm: several core tools, a handful of respected blogs, and a few incident write-ups that made everyone slightly uncomfortable in a useful way. Now it feels like a firehose aimed directly at the on-call rotation. DevOps teams now have more information than they can reasonably track. Critical updates are […]
How Open Source Dependency and Repo Attacks Compromise DevOps Pipelines and How to Stay Safe
Modern applications rely on open source components for up to 90% of their code, creating a vast attack surface dominated by inhemalicious supply chain injections. High-profile incidents like Log4j and the sabotage of colors.js highlight that traditional scanning often fails to detect sophisticated “protestware” or dependency confusion, necessitating 19 practical controls focused on strict intake governance, dependency pinning, and behavioral monitoring to secure the development lifecycle.
The MLSecOps Era: Why DevOps Teams Must Care about Prompt Security
AI-driven software delivery introduces new risks, especially prompt manipulation within CI/CD workflows. This article details the emerging fields of PromptOps and MLSecOps and offers practical strategies for securing prompts, models, and pipelines.
An Experience-Based Guide to Choosing the Right DevOps Provider in 2026
Selecting the right DevOps partner is critical for accelerating software delivery, reducing costs, and maintaining reliability. This guide outlines a four-phase approach — from internal preparation to final agreements — to help businesses evaluate, vet, and build long-term success with trusted DevOps service providers.
Mobile Apps Are Under Attack — And App Stores Will Not Protect You
Advanced tactics allow attackers to break into mobile apps from the inside, bypass authentication systems, and compromise sensitive user information through deepfake-powered identity fraud.
Ensuring Application Security from Design to Operation with DevSecOps
Safe development is critical for any company that creates software, whether for its own use or for others. DevSecOps principles focus on automating information security processes and introducing security measures early in software development. DevSecOps is extremely important these days as, according to recent surveys, more than 99% of tech professionals report that, on average, […]