


AWS AI Agent Surfaces Recommendations to Optimize Cloud Computing Environments
Amazon Web Services (AWS) today made available a preview of an artificial intelligence (AI) agent that surfaces recommendations to optimize cost, security, performance and resilience based on the business objectives an organization defines. Jill Fariss, vice president of AWS Support, said the AWS Well-Architected Agent generates code that can be implemented via a command line […]
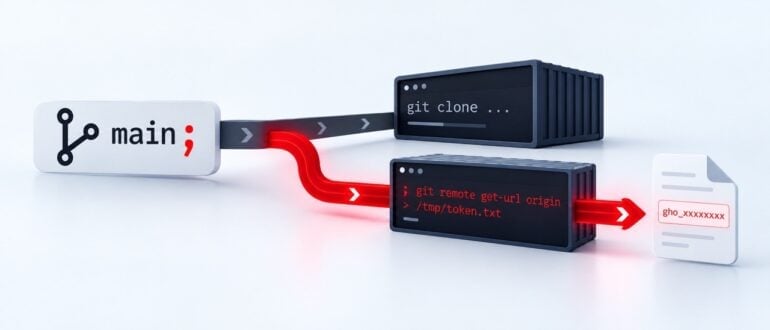
A Semicolon in a Branch Name Was All It Took to Steal an AI Agent’s GitHub Token
AI coding agents don’t just suggest code anymore. Tools like OpenAI’s Codex spin up a real container, clone a real repository, and authenticate with a real GitHub credential to get the job done — which means every agent your team wires up is also a new privileged identity, holding real access, running with comparatively little […]

Leaked GitLab Email Tokens Can Reach Code, Secrets and CI/CD Pipelines
Security researchers have uncovered a GitLab behavior that could let attackers use a leaked project email address to push code, trigger CI/CD jobs and reach other repositories accessible to the address owner. Aikido Security researcher Joe Leon detailed the attack path this week in a blog post after reporting it to GitLab earlier this year. […]

Why Plan Review Stopped Working
The control that held your infrastructure together was plan review, meaning a person reading a diff and deciding whether to approve it. Not the policy document and not the pipeline configuration. It worked because change arrived at human speed. That condition no longer holds. An agent opens 40 pull requests before lunch. Reviewers approve them […]

TeamPCP Supply Chain Attack Leads to CrowdSec Source Code Being Stolen
CrowdSec says attackers stole source code from about 170 private GitHub repositories after a TanStack npm supply chain attack exposed an OAuth token tied to a former employee.

Flaw in DeepSeek Harness AI Coding Tool Let Agents Disable Their Sandbox
News of the now-fixed vulnerability comes amid growing concerns that AI vendors do not in have complete control of their autonomous agents.

JFrog Moves to Secure Agentic Engineering Workflows
JFrog today at its swampUP 2026 conference added a zero touch remediation capability that ensures the most secure version of a binary is provided even when application developers request a version that has known vulnerabilities. Additionally, JFrog is adding tools and capabilities to secure artificial intelligence (AI) agents that have been embedded within a DevOps […]

From Operator to Agent Manager: The Real Shift in Network Engineering
I’ve been saying for ten years that network automation was three years away from being the only way to do things. Every year I moved the goalposts, because the data never caught up to the rhetoric. After a decade of scripts, YAML, Ansible, Terraform, and every NetDevOps framework we could throw at the problem, roughly […]

Cybersecurity Researchers Uncover Flaw in Google AI Coding Tool
Cybersecurity researchers from Pillar Security this week revealed how a prompt injection inserted into a GitHub repository was used to gain Editor-level access to an internal Google Cloud project using a flaw in the command line interface (CLI) of an artificial intelligence (AI) coding tool that Google provides. Dan Lisichkin, a cybersecurity researcher for Pillar […]

Sonar AI Agent Discovers Vulnerabilities Hidden in Business Logic Workflows
Sonar today made available an artificial intelligence (AI) agent designed to discover vulnerabilities and business logic flaws that pose the greatest risk to an organization should they be exploited. The SonarQube Hunter Agent first analyzes an entire codebase to find three categories of flaws: broken access control, business-logic vulnerabilities, and authentication or session-management issues. Satinder […]

Hackers Target Popular arrayref Rust Crate in Supply-Chain Attack
Security researchers are sorting through a complex, stealthy, and fast-moving supply-chain attack aimed at pushing information-stealing malware by compromising the account of the maintainer of multiple Rust crates and introducing four more attacker-owned crates. In addition, researchers with Wiz wrote that there also appears to be overlap with supply chain campaigns run by nation-state actors […]

npm v12 Shuts Down a Popular Malware Trick — But the Threat Isn’t Going Away
For years, one of the easiest ways to sneak malware onto a developer’s machine has been to hide in plain sight. Install a package from npm, and any lifecycle script bundled with it runs automatically — no review, no approval, no second look. Attackers have known this for a long time, and they’ve used it […]

Critical Flaw in isolated-vm Can Lead to Sandbox Escape, RCE Threat
Developers for years have been using vm2, an open-source Node.js library, to run untrusted JavaScript inside a secure and isolated sandbox environment. It uses Node.js’s built-in modules and JavaScript Proxies and lets developers whitelist particular built-in Node modules or limit what the script can access. During that time, vm2 has been the default for safely […]
GitHub Sharpens CodeQL’s Eye on Actions Workflows and Modern JavaScript
GitHub Actions pipelines have become one of the quieter attack surfaces in software development. They pull in third-party actions, cache dependencies, and pass secrets between jobs, often without anyone reviewing the workflow file as closely as they’d review application code. That gap is exactly where cache-poisoning and output-clobbering attacks live, and it’s why GitHub keeps […]

Cloudsmith Extends Policies and Controls to Secure Application Binaries
Cloudsmith this week revealed it has expanded the policy management and continuous risk detection capabilities it makes available within its software artifact management platform to now include policy templates, cooldown policies, and expanded evaluation triggers. Alison Sickelka, vice president of product for Cloudsmith, said these additions to the platform will make it simpler to prevent […]

Why Enterprise AI Infrastructure Is Becoming a DevOps Problem
Most enterprise AI projects start with retrieval. You connect Jira, Confluence, SharePoint, and Slack. Maybe a few internal databases nobody has touched in five years. You tune embeddings, optimize chunking, wire up a vector database, and convince yourself you’ve built an AI-powered knowledge system. Then the model server crashes. And suddenly, you discover the uncomfortable […]

Attackers Can Exploit a Claude Code RCE Flaw to Take Command of System
A dangerous vulnerability found in Anthropic’s popular Claude Code developer model could have allowed bad actors to grab control of a victim’s system by luring them into clicking on a crafted malicious deeplink. Once in, the attacker could exploit the remote code execution (RCE) security flaw to execute arbitrary commands – such as shell commands […]
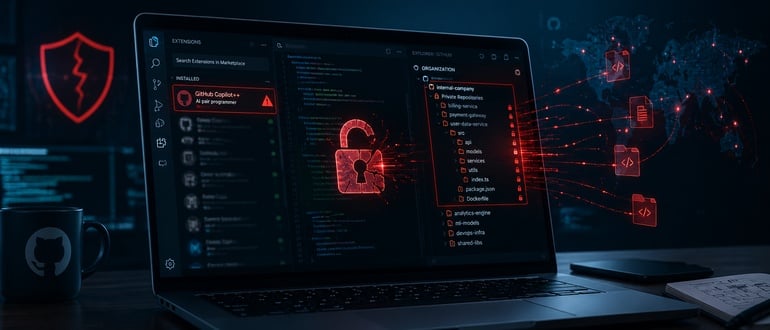
GitHub Breach Tied to Malicious VS Code Extension Exposes Thousands of Internal Repositories
GitHub says attackers accessed thousands of internal repositories after a company employee’s device was compromised through a malicious Visual Studio Code extension, though the company said it has removed the malicious extension, isolated the compromised endpoint, and launched an investigation. The company confirmed that approximately 3,800 internal repositories were affected. GitHub stated that investigators have […]

Red Hat Previews AI Agent Integration with Ansible Automation Platform
Red Hat today revealed it is extending the reach of its Ansible Automation Platform for IT operations to artificial intelligence (AI) agents, in addition to making it simpler to build AI agents using existing application development tools. Announced at the Red Hat Summit conference, version 2.7 of the Ansible Automation Platform adds a technology preview […]

Why Senior Engineers Still Do Manual Work in Highly Automated Environments
Automation has been part of enterprise IT for many years, and in many environments, it has grown into an extensive network of interdependent workflows that keep routine operations running smoothly. Scripts provision accounts, automated workflows manage cloud resources, orchestration tools coordinate ITSM processes, and AI-driven tools help employees across the organization complete tasks more efficiently. […]
Cyber Threats to DevOps Platforms Rising Fast, GitProtect Report Finds
The number of incidents targeting DevOps platforms grew 21% in 2025, but the amount of downtime jumped almost 95%, the security firm said.

When AI Goes Really, Really Wrong: How PocketOS Lost All Its Data
You can’t make this crap up. You just wish you could. Jer Crane, founder of the small vertical software company, PocketOS, reported on X that the AI Cursor coding agent and a Railway backup misconfiguration combined to briefly wipe out the company’s car‑rental customer production data. Not some of the data. All of it. That’s […]

Sophisticated Supply Chain Attack Targeting Trivy Expands to Checkmarx, LiteLLM
The supply chain attack that compromised Aqua Security’s Trivy open source security vulnerability scanner and its associated GitHub Actions earlier this month continues to expand, with software development tools from Checkmarx and LiteLLM being the latest victims of the sophisticated campaign. The threat group behind it, TeamPCP, is using the attacks to create persistence and […]
Showing the 24 most recent articles. Additional archive pages are not yet available.