



Blitzy Makes Sandbox for Reverse Engineering Code Available at No Cost
Blitzy has made available a sandbox where DevOps teams can reverse-engineer up to one million lines of code, generate up to 25,000 lines of tested end-to-end code, and identify security vulnerabilities across a codebase at no cost. Dan Ochs, director of AI solutions consulting for Blitzy, said the provider’s Proactive Insights platform uses multiple artificial […]

DevSecOps Teams as Partners in Secure Software Delivery
DevSecOps teams can reduce last-minute release delays by shifting security decisions earlier, improving guardrails, clarifying ownership and making findings actionable.

TeamPCP Supply Chain Attack Leads to CrowdSec Source Code Being Stolen
CrowdSec says attackers stole source code from about 170 private GitHub repositories after a TanStack npm supply chain attack exposed an OAuth token tied to a former employee.

New npm Threat Bypasses Install Script Protections
A malicious npm package that has been downloaded millions of times comes with a new way of spreading the malware that makes it easier to bypass security protections, say researchers with security vendor Checkmarx. Rather than using more common preinstall or postinstall scripts, the bad actors instead created a malicious package – indexed-btree – that […]

Harness Previews Revamped Platform for the Agentic Engineering Era
Harness today previewed a revamped user interface for its platform for managing software deployments that makes it simpler for software engineers to manage teams of artificial intelligence (AI) agents using a forthcoming Harness Software Factory platform. Speaking at an {unscripted} NYC 2026 event, Harness CEO Jyoti Bansal told conference attendees the Harness Software Factory will […]

Flaw in DeepSeek Harness AI Coding Tool Let Agents Disable Their Sandbox
News of the now-fixed vulnerability comes amid growing concerns that AI vendors do not in have complete control of their autonomous agents.

Certificate Renewal Is a Deployment Workflow, Not a Cron Job
Certificate renewal is often treated as a scheduled task: run an ACME client, obtain a new certificate, and move on. In practice, that view is too narrow for production systems. A certificate is not useful because it exists on disk. It is useful because the right service is presenting it to users. Between issuance and […]

Why “Tokenmaxxing” Was Always the Wrong Way for Developers to Measure AI Productivity
The term “tokenmaxxing” left the developer lexicon just as quickly as it arrived, and like most viral technology concepts, it means different things depending on who’s using it. In practice, the term is being applied in two ways: maximizing total token consumption as a proxy for AI adoption and effort, or optimizing output per token […]

Critical Flaw in isolated-vm Can Lead to Sandbox Escape, RCE Threat
Developers for years have been using vm2, an open-source Node.js library, to run untrusted JavaScript inside a secure and isolated sandbox environment. It uses Node.js’s built-in modules and JavaScript Proxies and lets developers whitelist particular built-in Node modules or limit what the script can access. During that time, vm2 has been the default for safely […]

Harness Adds AI Agents to Automate DevSecOps Workflows at Machine Speed
Harness today added multiple artificial intelligence (AI) agents and a virtual patching capability to its portfolio to automate DevSecOps workflows at a time when the number of vulnerabilities being discovered in code continues to exponentially increase. The AI agents include one that has been added to the static application security testing (SAST) tool that Harness […]
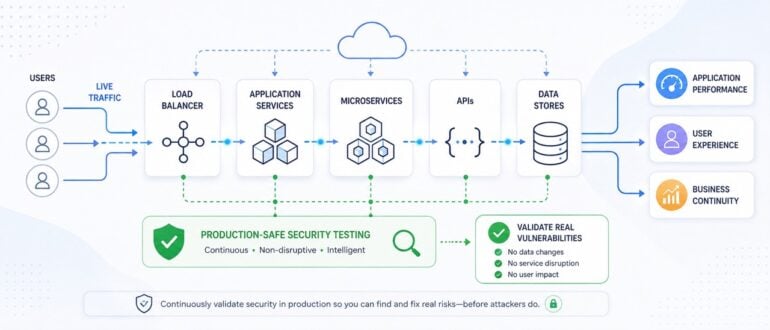
Production-Safe Testing: The Missing Piece in Most DevSecOps Strategies
Most DevSecOps teams invest heavily in security before deployment, yet attackers target the production environment where applications, APIs, and user behavior are constantly changing. If security validation stops before release, critical risks can remain hidden until they are exploited. The gap is more common than many organizations realize. A survey found that over 70% of […]

LiteLLM Attack Affected 2,500 Companies, 434,000 CI/CD Pipelines: CloudSEK
The massive supply-chain attack that compromised LiteLLM in the spring affected more than 2,500 companies and exposed about 434,000 CI/CD pipelines, with victims ranging from top-tier IT and AI companies to cybersecurity firms, SaaS, and enterprises. It rolled up a lot of victims, but also was a high-profile example of the growing trend of threat […]
‘Flooding Dropper’ Is Hitting npm With a Tidal Wave of Malicious Packages
Threat researchers at Sonatype are warning developers of an expanding campaign that is generating a wide range of npm accounts and dropping small numbers of malicious packages from each one, essentially flooding the zone with a broadly distributed and automated campaign to make it difficult for defenders to keep up. So far, the campaign – […]

RapidFort Extends Open Source Software Security Reach to Runtime Environments
RapidFort today at the Black Hat USA conference announced it has extended its ability to secure open source software to the runtimes that DevOps teams deploy in production environments. Michael Wood, chief marketing officer for RapidFort, said the RapidFort Runtime platform makes it possible to now monitor open source software deployed within a container image […]

Fast-Moving Shai-Hulud Attack Infects npm Packages with 2 Billion Monthly Downloads
Researchers at Aikido Security and Endor Labs are tracking a fast-spreading supply-chain attack that is compromising a wide range of npm software packages that combined have more than 2 billion installs a month and is stealing a wide range of secrets and other information. According to Ilyas Makari, malware researcher with Aikido, the bad actor […]

FakeGit Targets AI Coding Agents with Malicious GitHub Repos
Threat actors continue to find new ways to incorporate AI into schemes aimed at luring developers into downloading malware from fake repositories. The latest example involves almost 7,600 malicious GitHub repositories that are being used to distribute a loader and an information-stealer. The FakeGit campaign is nothing new, with Oleg Zaytsev, lead security researcher with […]
Security Risks from AI Coding Agents Expand Beyond the Sandbox: Pillar
AI coding assistants have become an essential part of developers’ work, automating many of the repetitive tasks – think boilerplate coding and scaffolding – that in the past ate up a lot of their time. More jobs can now get done faster. That said, such agents also represent a significant security risk, making developers – […]

Signed, Attested, and Malicious: The Software Supply Chain Has a Deepfake Problem
A developer pulls a package from a reliable repo. It is signed, has provenance, and has been scanned. And then…it contains malware. That is no longer hypothetical. When the Miasma worm tore through the @redhat-cloud-services npm namespace in June, its malicious releases carried real SLSA provenance, because they were built in Red Hat’s own GitHub […]

xAI Open-Sources Grok Build Coding Agent After Cloud Upload Exposes SSH Keys, Repos
xAI has published the full source code for Grok Build, its terminal-based AI coding agent, on GitHub under an Apache 2.0 license. The release lands three days after a security researcher showed the tool quietly shipping entire developer repositories — SSH keys and password databases included — to a Google Cloud bucket xAI controls. The […]

From AI Hype to AI Assurance: How Engineering Teams Can Safely Ship AI-Enabled Software
AI has moved very quickly from experimentation to production. A few years ago, many organizations were still asking whether AI could improve their products or internal workflows. Today, the question is different: how can teams ship AI-enabled software safely, reliably, and responsibly? That shift matters because AI is no longer just a research project or […]

GitHub API Abuse, ‘Ghost’ Accounts Part of Malicious Efforts to Map Organizations
Datadog researchers uncover months-long overlapping campaigns to scrape data about companies and their developers.

‘HalluSquatting’ Compromises AI Coding Agents to Install Malware, Create Botnets
Hallucinations have been an ongoing problem since OpenAI first introduced its ChatGPT chatbot in November 2022, highlighting generative AI’s tendency to generate plausible but false or misleading information and its inability to just say “I don’t know.” They can lead to embarrassing or uncomfortable moments. However, security researchers in Israel have found that the large […]

How to Build a DevSecOps CI/CD Pipeline on Azure With GitHub Actions
Fix security problems when they’re cheap to fix, which is before the code is deployed. A pipeline that enforces this automatically is what makes that principle real.
Showing the 24 most recent articles. Additional archive pages are not yet available.