


Latest from Samuel
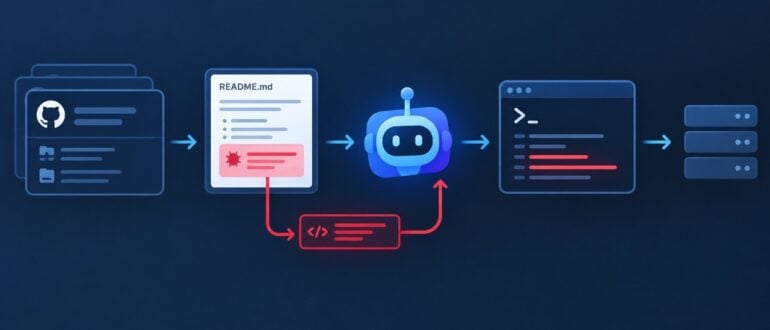
When AI Coding Agents Become Malware Delivery Systems
AI coding agents are becoming part of everyday development work. Developers use them to find libraries, configure projects, troubleshoot installation problems, and set up new tools. An agent can search GitHub, read project documentation, and run commands without the developer having to work through every step manually. That convenience is creating another security concern for […]
Aug 27, 2026 · 3 minAll articles by Samuel Ogbonna
Showing 1–10Why Standardized Developer Environments Still Break DevOps Workflows
Standardized developer environments promise to eliminate one of software engineering’s oldest explanations: “It works on my machine.” By packaging approved runtimes, dependencies and tools into containers, virtual machines or cloud workspaces, organizations expect every developer to start from the same foundation. The approach delivers clear benefits. It reduces onboarding time, minimizes dependency conflicts and makes […]
Why Developer Workstations Have Become a Critical Part of the Software Supply Chain
For years, software supply-chain security discussions focused on centralized infrastructure such as build servers, package registries, and CI/CD systems. Recent attacks suggest that this view is incomplete. The Megalodon campaign injected malicious GitHub Actions workflows into thousands of repositories, while a separate incident involving a malicious Visual Studio Code extension demonstrated how a single compromised […]
From Phishing to Vishing: Why DevSecOps Must Rethink Communication Security
Key Takeaways: Vishing is the new frontline threat: Attackers are shifting from emails to phone-based scams, using AI and social engineering to bypass traditional security controls. DevSecOps must expand its scope: Securing code is no longer enough; communication channels like voice, chat, and messaging must be integrated into threat models and security pipelines. Human and […]
Why Endpoint Protection Matters More than Ever in CI/CD Environments
CI/CD environments depend on far more than repositories and deployment infrastructure. Developer endpoints hold sensitive data: cloud credentials, SSH keys, deployment permissions, direct access to internal systems. Endpoint security and control are part of daily operational risk management. Engineering teams are shifting more and more toward distributed workflows, so discussions around CI/CD security include the […]
How to Manage Operations in DevOps Using Modern Technology
How modern DevOps teams manage operations using automation, observability, AIOps and self-service to reduce toil and improve reliability.
When Customer-Facing Systems Fail: How Incident Response and Observability Reduce MTTR
In a world of microservices and real-time interactions, MTTR is the ultimate metric for brand protection. Learn how observability and resilient architecture drive faster incident response.
The Hidden Security Risks in Modern JavaScript Frameworks and How React Teams Can Reduce Them
React and modern JavaScript frameworks accelerate development—but hide serious security risks. Learn where vulnerabilities come from and how to reduce client-side attack surfaces.
Patch or Perish: The Brutal Truth About Vulnerability Management in 2025
Vulnerability management in 2025 is overwhelmed by escalating CVEs and costly breaches; organizations must shift from slow, manual patching to continuous, risk-based, AI-powered remediation to stay secure.
How Cybersecurity Teams Can Work Better with DevOps
DevOps teams move fast, but security can lag without the right approach. Often, cybersecurity and DevOps teams work separately, and that could lead to problems. To fix this, organizations must shift from viewing security as a checkpoint to embedding it in DevOps at every step. This article explores how to infuse security in DevOps from […]