



Why Self-Healing Tests Need a Deployment Gate
When an end-to-end test fails after a front-end change, the repair often looks routine. A class name changed. A button moved. A selector that used to be unique now matches two elements. A self-healing system inspects the page, proposes a new locator, reruns the test, and gets a green result. That green result is useful, […]
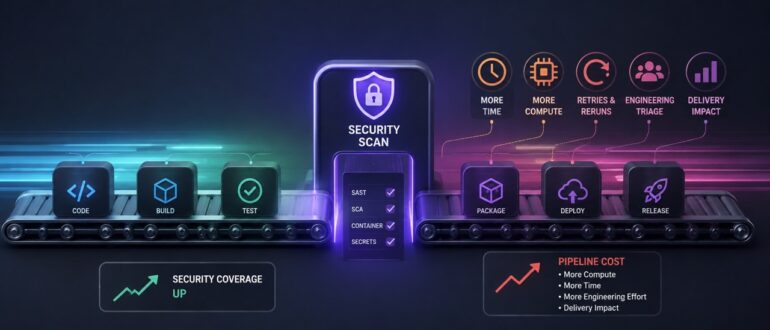
Is Your New DevSecOps Tooling Reducing Work Or Just Adding to It?
Security belongs in the software delivery pipeline. The harder question is where, how often and at what cost. Many pipeline teams eventually add security scanning to CI/CD, and relatively few go back afterward to measure what it actually cost the delivery process. Security coverage went up. Something else changed too, and it is rarely measured […]
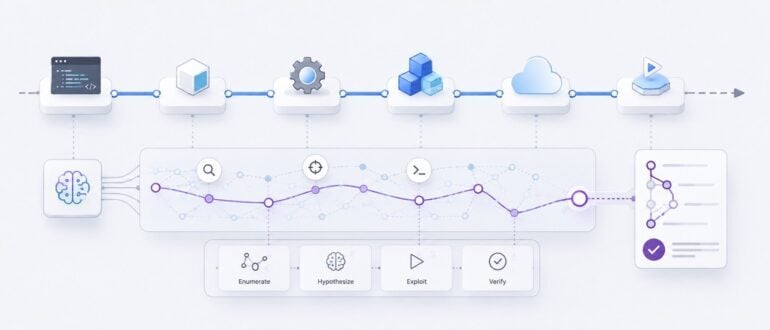
Why CI/CD Security Testing Is Going Autonomous (and Why It Should Stay Local)
Continuous integration and delivery changed the tempo of software. Teams merge dozens of times a day, infrastructure is redefined on every commit, and a new build can reach production in minutes. Security testing never caught up with that tempo. It still lives in two modes that both fight the pipeline instead of moving with it. […]

LiteLLM Attack Affected 2,500 Companies, 434,000 CI/CD Pipelines: CloudSEK
The massive supply-chain attack that compromised LiteLLM in the spring affected more than 2,500 companies and exposed about 434,000 CI/CD pipelines, with victims ranging from top-tier IT and AI companies to cybersecurity firms, SaaS, and enterprises. It rolled up a lot of victims, but also was a high-profile example of the growing trend of threat […]
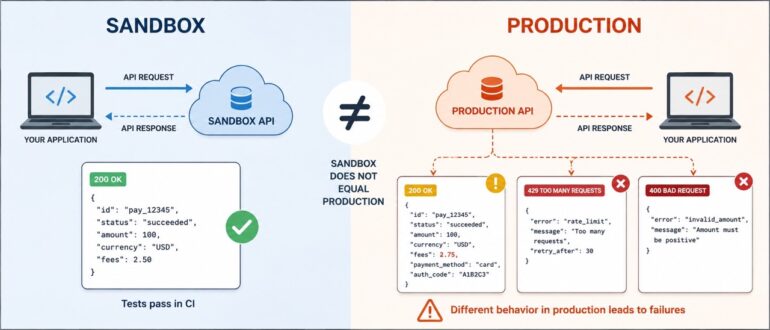
Sandbox Testing for API-Heavy Systems: What Changes When You Don’t Own the Dependency
Sandbox testing works well when your team controls both sides of the integration. You define the service, you define the mock, you know exactly what the sandbox should return. That setup holds up fine for internal microservices and first-party APIs. It starts to break down when you don’t own the dependency. Payment processors, identity providers, […]

RapidFort Extends Open Source Software Security Reach to Runtime Environments
RapidFort today at the Black Hat USA conference announced it has extended its ability to secure open source software to the runtimes that DevOps teams deploy in production environments. Michael Wood, chief marketing officer for RapidFort, said the RapidFort Runtime platform makes it possible to now monitor open source software deployed within a container image […]

Fast-Moving Shai-Hulud Attack Infects npm Packages with 2 Billion Monthly Downloads
Researchers at Aikido Security and Endor Labs are tracking a fast-spreading supply-chain attack that is compromising a wide range of npm software packages that combined have more than 2 billion installs a month and is stealing a wide range of secrets and other information. According to Ilyas Makari, malware researcher with Aikido, the bad actor […]

These are 10 CI/CD Pipeline Mistakes That Slow Down Engineering Teams
Continuous software delivery in the digital age has come to depend on CI/CD pipelines. They enable engineering teams to rapidly develop, test, and deploy code while keeping it highly usable and consistent across environments. CI/CD pipelines, however, can themselves become a source of friction as systems start at a small scale and become more complex. […]

FakeGit Targets AI Coding Agents with Malicious GitHub Repos
Threat actors continue to find new ways to incorporate AI into schemes aimed at luring developers into downloading malware from fake repositories. The latest example involves almost 7,600 malicious GitHub repositories that are being used to distribute a loader and an information-stealer. The FakeGit campaign is nothing new, with Oleg Zaytsev, lead security researcher with […]
Security Risks from AI Coding Agents Expand Beyond the Sandbox: Pillar
AI coding assistants have become an essential part of developers’ work, automating many of the repetitive tasks – think boilerplate coding and scaffolding – that in the past ate up a lot of their time. More jobs can now get done faster. That said, such agents also represent a significant security risk, making developers – […]
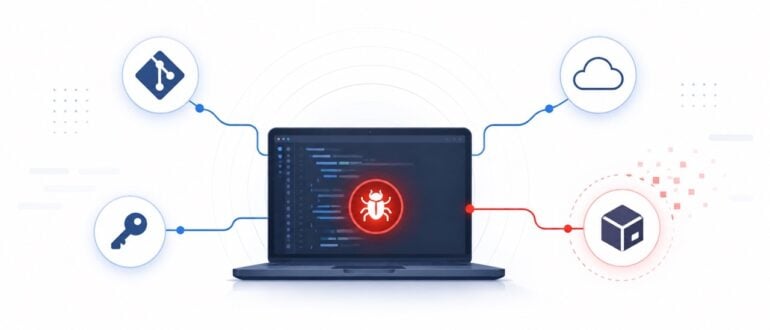
Why Developer Workstations Have Become a Critical Part of the Software Supply Chain
For years, software supply-chain security discussions focused on centralized infrastructure such as build servers, package registries, and CI/CD systems. Recent attacks suggest that this view is incomplete. The Megalodon campaign injected malicious GitHub Actions workflows into thousands of repositories, while a separate incident involving a malicious Visual Studio Code extension demonstrated how a single compromised […]

‘HalluSquatting’ Compromises AI Coding Agents to Install Malware, Create Botnets
Hallucinations have been an ongoing problem since OpenAI first introduced its ChatGPT chatbot in November 2022, highlighting generative AI’s tendency to generate plausible but false or misleading information and its inability to just say “I don’t know.” They can lead to embarrassing or uncomfortable moments. However, security researchers in Israel have found that the large […]

North Korea Expands the Reach of PolinRider Supply Chain Attack Campaign
The North Korean-sponsored threat groups behind the long-running fake interview scams targeting developers are expanding the PolinRider supply chain campaign that has escalated over the past several months. Reports from cybersecurity vendors Socket and Rescana found that two groups linked to the Democratic People’s Republic of Korea (DPRK) have published at least 108 malicious packages […]

How AI is Revamping DevSecOps Processes
Artificial Intelligence is pushing DevSecOps into a new phase where security is no longer just about detecting vulnerabilities, but increasingly about resolving them automatically within the flow of software delivery. As many organizations are discovering, DevSecOps historically gave teams visibility into risk. AI is now turning that visibility into automated remediation. This evolution has taken […]

Block Details Builderbot Framework for Orchestrating AI Agents Across SDLC
The software engineers at Block have developed an orchestration layer they are using to manage artificial intelligence (AI) agents that have been trained to automate multiple tasks across their software development lifecycle (SDLC). Based on goose, an open source agent framework the company developed and contributed to the Agentic AI Foundation (AAIF), the Builderbot orchestration […]
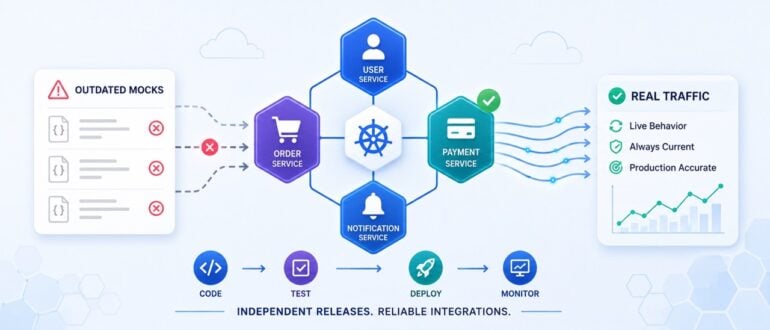
How Independent Service Deployments Expose the Limits of Conventional Regression Testing Tools
The architectural shift to independently deployable services was supposed to make software delivery faster and less risky. In many aspects, it has. Teams can ship a change to one service without coordinating a release across the entire system. A bug fix in the payment service does not require a synchronized deployment with the notification service, […]

Lightrun Adds Ability to Assess Impact Pull Request Will Have in Production
Lightrun is providing early access to an ability to verify whether a pull request (PR) will actually run in a production environment as part of its artificial intelligence (AI) platform for automating site reliability engineering (SRE) workflows. Company CTO Leonid Blouvshtein said the Runtime Aware PR Verifier enables DevOps teams to assess the impact a […]

Harness Adds Autonomous AI Agents to Automate DevOps Workflows
Harness today is providing DevOps teams with an ability to build and deploy autonomous artificial intelligence (AI) agents that automate the delivery of code to production environments. Trevor Stuart, a senior vice president and general manager at Harness, said the Autonomous Worker Agents eliminate the need for fixed scripts with custom AI agents or ones […]
Modernization Is Not Migration
Modernization worked only if the platform became easier to change, easier to understand and safer to run under pressure. That is not a philosophical position — it is a measurable one.

Salesforce vs Dynamics 365 CE DevOps: A Practical Comparison for Enterprise Teams
Most organizations running CRM platforms eventually face the same challenge: how to deploy changes safely, consistently, and quickly. While Salesforce and Dynamics 365 Customer Engagement (CE) support modern DevOps practices, they approach application lifecycle management differently. Understanding these differences can help teams design more effective deployment pipelines and avoid common release issues. As these platforms […]

Newly Appointed CloudBees CEO Charts Agentic AI Engineering Course
The newly appointed CEO of CloudBees, Mo Plassnig, says that as the agentic artificial intelligence (AI) era dawns, the time has come to reinvent software engineering in a way that moves beyond human-centric tooling. Plassnig, who earlier this month succeeded Anuj Kapur, joins CloudBees from Immuta, a provider of a data security and governance platform, […]

Why AI Testing Must Live Inside Your CI/CD Pipeline
Here is a situation most engineering leaders recognize. You roll out AI coding tools. Features ship faster. Developers are more productive. Then, a few months in, you realize something unexpected: the engineers you most wanted to free up are busier than ever. They are reviewing PRs, firefighting regressions, juggling a dozen half-shipped features and the […]

Why Endpoint Protection Matters More than Ever in CI/CD Environments
CI/CD environments depend on far more than repositories and deployment infrastructure. Developer endpoints hold sensitive data: cloud credentials, SSH keys, deployment permissions, direct access to internal systems. Endpoint security and control are part of daily operational risk management. Engineering teams are shifting more and more toward distributed workflows, so discussions around CI/CD security include the […]
Showing the 24 most recent articles. Additional archive pages are not yet available.