



Attaching Evidence to Alerts: an Enrichment Sidecar for Alertmanager
Every on-call engineer knows the ritual. A page lands in Slack: the 5xx rate on a service is above the threshold. The message tells you that something is wrong and nothing about what. So you open Kibana or Loki in another tab, set the time window to the last few minutes, filter by the service, […]

Secrets Sprawl and Rotation: A Practical Vault Management Playbook
In 2025 alone, security firm GitGuardian detected 28.65 million new hardcoded secrets exposed in public GitHub commits — a 34% increase year over year and the largest single-year jump the company has recorded in five years of publishing its annual State of Secrets Sprawl report. Since 2021, that number has grown 152%, far outpacing the […]
AI Is Taking on Entry-Level Engineering Work. Who Trains the Young Engineers?
When I started my career on a support desk, I dealt with failed logins, missing permissions and recurring system errors every day. The work was repetitive, but repetition taught me to spot patterns, test assumptions and look beyond the symptom a user reported. Over time, I was resolving around 90% of incidents at first contact. […]

Federated Query at Petabyte Scale: A Deployment Pattern for a Governed AI-Agent Data Layer
A federated query architecture can reduce data duplication and latency while creating a governed, auditable data layer that enterprise AI agents can safely access.

Security Teams Are Fixing Vulnerabilities Faster Than Ever. So Why Is Software Getting Riskier?
AI is speeding up dependency decisions, making point-of-selection security essential for reducing vulnerable components, downstream tickets and avoidable rework.

Availability Should Follow the Workload, Not the Infrastructure
Platform engineering has automated deployment but not recovery. The next maturity curve is intelligent operations that automate routine production decisions and resilience.

Taste, Discernment, and Judgment Have Become Must-Have Engineering Skills
AI coding agents make code generation cheap, shifting engineering value toward standards, deterministic quality gates, contextual review and human judgment about what should ship.

QA Automation Frameworks for Enterprise Applications
Modern enterprise applications demand testing strategies that can keep pace with continuous delivery, distributed architectures, and increasingly complex deployment pipelines. Traditional manual testing approaches often become a bottleneck as engineering teams scale their applications and release software more frequently. This article explores the essential building blocks of an enterprise-grade QA automation framework, focusing on maintainability, […]

AI Is Breaking Developers’ Traditional Game Testing Playbook
Game testing has always been an unpredictability problem for developers. Players move in the wrong direction, trigger events out of order, or combine mechanics no designer anticipated. Even so, developers could usually define the rules governing the world and check whether the game followed them. AI is making that harder. NPCs now react to changing […]

How to Move AI SRE Agents From Demo to Production
An AI agent that works on an engineer’s laptop can feel like a breakthrough. It can read logs, query observability tools, inspect cloud resources and connect a failed deployment to a bad configuration change in minutes. For a single investigation, under close human supervision, that is real progress. It is also the easy part. The […]
From Software Supply Chains to AI Vulnerabilities: Why Neither Solves Enterprise Linux Security
For nearly a decade, cybersecurity has been dominated by one overarching concern: securing the software supply chain. Organizations invested heavily in Software Bills of Materials (SBOMs), artifact signing, provenance frameworks, reproducible builds, and vulnerability scanners capable of identifying compromised dependencies before software reached production. The software supply chain became the industry’s focal point, accelerated by […]
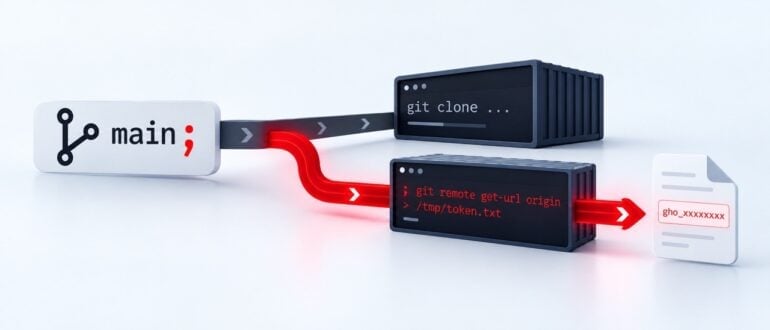
A Semicolon in a Branch Name Was All It Took to Steal an AI Agent’s GitHub Token
AI coding agents don’t just suggest code anymore. Tools like OpenAI’s Codex spin up a real container, clone a real repository, and authenticate with a real GitHub credential to get the job done — which means every agent your team wires up is also a new privileged identity, holding real access, running with comparatively little […]

Dependency Mocking Approach That Gets More Accurate as Your Services Deploy More Often
Traffic-based dependency mocking turns frequent upstream deployments into opportunities to refresh mocks from real behavior and reduce integration test drift.

Why Old Azure DevOps Releases Survive a Pipeline Cutover
Old Azure DevOps Classic releases can retain retired deployment tasks, Helm names, image paths and variables long after a pipeline cutover, leaving stale redeploy paths active.

DevSecOps Teams as Partners in Secure Software Delivery
DevSecOps teams can reduce last-minute release delays by shifting security decisions earlier, improving guardrails, clarifying ownership and making findings actionable.

Why Plan Review Stopped Working
The control that held your infrastructure together was plan review, meaning a person reading a diff and deciding whether to approve it. Not the policy document and not the pipeline configuration. It worked because change arrived at human speed. That condition no longer holds. An agent opens 40 pull requests before lunch. Reviewers approve them […]

What I Learned Building Cloud-Portable Services Across Multiple Providers
Multi-cloud strategies often stumble over provider-specific behavior. A layered abstraction built on official SDKs can normalize differences while preserving access to valuable native capabilities.

The Observability Tax: When Monitoring Costs Exceed Downtime Costs
Observability costs can spiral when teams collect more telemetry than they actually use. A more mature approach prioritizes the data that directly improves incident detection, diagnosis and recovery.

Why Shift Left is Dead
AI-driven development is exposing risks before code is written, forcing security teams to move beyond shift-left and govern agents, prompts, tools and data across the entire development lifecycle.

IT Outsourcing Versus In-House Development
The debate isn’t new — but the stakes are. In 2026, the gap between companies that get this decision right and those that don’t is measured in product cycles, burn rate, and competitive ground lost to faster-moving teams. Most engineering leaders frame the question as a cost problem. It isn’t. It’s a capability and velocity […]

Why Your CI/CD Pipeline Is Your Most Unprotected Attack Surface
CI/CD pipelines often hold privileged credentials, execute third-party code and connect directly to production, making pipeline security one of the most overlooked risks in modern DevOps.
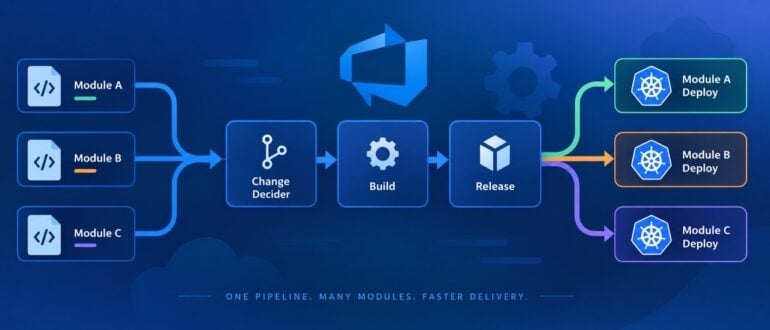
How I Consolidated Duplicate Delivery Pipelines With Parameters and Build Tags
Two modules in a repository had near-identical Azure DevOps build and release definitions. A third would have required another pair. The delivery chain used five definitions: one change decider, two builds, and two releases. I consolidated it into one decider, one generic build, and one release with a deployment stage for each onboarded module. The […]

Can Rust Improve Real Django API Performance? Testing Django-Bolt Beyond Synthetic Benchmarks
Django-Bolt uses Rust to accelerate Django request handling, but real-world gains depend on database work, authentication, serialization and where an API actually spends its time.
Showing the 24 most recent articles. Additional archive pages are not yet available.