



LiteLLM Attack Affected 2,500 Companies, 434,000 CI/CD Pipelines: CloudSEK
The massive supply-chain attack that compromised LiteLLM in the spring affected more than 2,500 companies and exposed about 434,000 CI/CD pipelines, with victims ranging from top-tier IT and AI companies to cybersecurity firms, SaaS, and enterprises. It rolled up a lot of victims, but also was a high-profile example of the growing trend of threat […]

Open Source Code Just as Secure as Proprietary Software—If You Manage It Right, Says CISA
Open source can be just as safe as proprietary software, though government agencies (and private enterprises) should take additional measures to secure it properly, according to a new guide published by the U.S. Cybersecurity and Infrastructure Security Agency (CISA). The report, “Open Source Software: Security Principles and Practices,” provides with guidance to help agencies comply […]

How AI is Revamping DevSecOps Processes
Artificial Intelligence is pushing DevSecOps into a new phase where security is no longer just about detecting vulnerabilities, but increasingly about resolving them automatically within the flow of software delivery. As many organizations are discovering, DevSecOps historically gave teams visibility into risk. AI is now turning that visibility into automated remediation. This evolution has taken […]

Platform Engineering vs. DevOps: Why This Is the Wrong Question
DevOps has done what it was supposed to do. It broke down the wall between development and operations, it made continuous delivery a normal expectation, it made shared ownership of production a cultural default, and it moved software delivery from a scheduled event to a continuous flow. The results reshaped how modern software gets built. […]
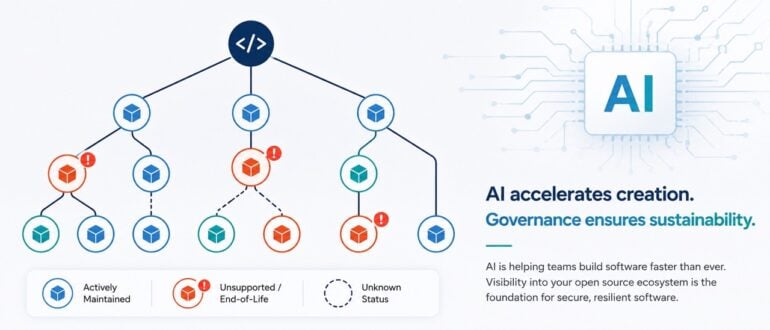
AI Is Exposing a Growing Blind Spot in Open Source Security
With AI, teams across organizations are now building internal applications faster than ever, often pulling in open source libraries and frameworks without much thought about long-term support, lifecycle management, or security ownership. An unintended consequence of this is that unsupported open source software (OSS) is quietly spreading across environments faster than security and engineering teams […]
Why Your Observability Stack Is Costing You More Than Your Cloud Bill
There’s a pattern playing out across engineering teams right now that nobody talks about openly: the tool meant to reduce operational complexity has quietly become one of the biggest line items on the infrastructure budget. Observability spending is out of control, and for most teams, it’s not because they’re monitoring too much. It’s because they’re […]

Why Your AI Agent is a Black Box and How to fix it With OpenTelemetry
You built the agent. It works in testing. Then it hits production and starts giving wrong answers, timing out or burning through your token budget, and you have no idea why. This is when developers discover that print statements and log files weren’t designed for this. LLM applications fail in ways that traditional tooling can’t see. A hallucination doesn’t throw […]
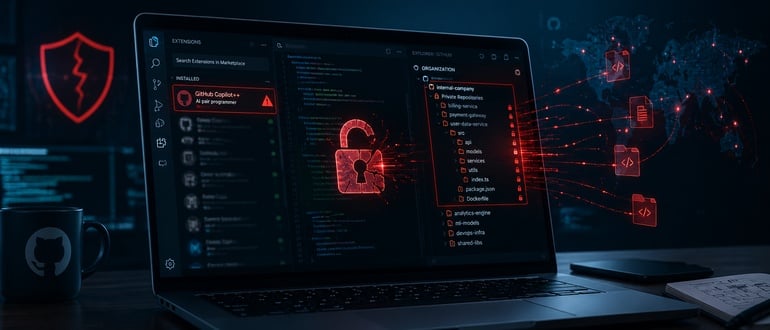
GitHub Breach Tied to Malicious VS Code Extension Exposes Thousands of Internal Repositories
GitHub says attackers accessed thousands of internal repositories after a company employee’s device was compromised through a malicious Visual Studio Code extension, though the company said it has removed the malicious extension, isolated the compromised endpoint, and launched an investigation. The company confirmed that approximately 3,800 internal repositories were affected. GitHub stated that investigators have […]

OpenSSF’s CRob: ‘The Runway Is Rapidly Running Out’ on EU CRA Readiness
The EU’s Cyber Resilience Act kicks into high gear this September, and companies are still clueless about how they must obey its strictures. MINNEAPOLIS — At Open Source Summit North America, Christopher “CRob” Robinson, Chief Security Architect for the Open Source Software Foundation (OpenSSF), spoke about the European Union’s (EU) Cyber Resilience Act (CRA). CRob […]

Why DevOps Is Critical for Modern Business Resilience
Today’s business world operates in a state of constant change. What the customer wants to buy changes quickly, new competitors appear overnight, and cyber threats are changing faster than ever. In this world, the concept of “resilience,” the ability to adapt, to overcome, and to continue to create value for the enterprise despite the changes, […]

Migration Observability: Measure Meaning, Not Movement
Traditional operational observability focuses on latency, errors, throughput and saturation. Migration observability needs a different category: Semantic drift.
How Open Source Dependency and Repo Attacks Compromise DevOps Pipelines and How to Stay Safe
Modern applications rely on open source components for up to 90% of their code, creating a vast attack surface dominated by inhemalicious supply chain injections. High-profile incidents like Log4j and the sabotage of colors.js highlight that traditional scanning often fails to detect sophisticated “protestware” or dependency confusion, necessitating 19 practical controls focused on strict intake governance, dependency pinning, and behavioral monitoring to secure the development lifecycle.

The Observability Bill is Coming Due – and AI Wrote Most of It
Observability has always had a data quality problem. AI coding agents just made it catastrophically worse. Shimmy sits down with the co-founders of Sawmills to dig into why unmanaged telemetry is the unglamorous DevOps crisis that is quietly killing budgets — and what an agentic telemetry management platform actually does about it.
Claude Code Security Finds the Bugs That Static Analysis Can’t — and Wall Street Noticed
Claude Code Security scans code like a human researcher, not a rule engine. Anthropic found 500+ decade-old bugs — and cybersecurity stocks felt it.

How Small Engineering Teams Can Improve Reliability Without Adding Process Overhead
Modern software teams are under constant pressure to ship faster while maintaining reliability. For small engineering teams, this balance can feel especially difficult. Limited resources, tight deadlines, and shared responsibilities often mean that reliability improvements are postponed in favor of feature delivery. The good news is that improving reliability does not require heavy frameworks, additional […]
Observability, SRE and Uptime in Telehealth Platforms: A DevOps Playbook
Virtual care went from nice to have to must have during the COVID-19 pandemic and while in-person visits are starting to pick up again, telemedicine is here to stay. Its growth will continue: health-tech companies are predicting the telemedicine market will be $143.49 billion by 2025 (it will be $167.74 billion in 2025 and $584.99 […]

When Metrics Overwhelm: How SREs Help Engineers Reclaim Focus
Observability promised insight but delivered alert fatigue. Learn how SREs are redefining observability to empower developers and restore real engineering value.

White Paper: The Future of DevSecOps in a Fully Autonomous CI/CD Pipeline
Abstract The growing complexity of modern software development and the increasing speed at which organizations need to deliver software have led to the widespread adoption of DevOps practices, particularly continuous integration/continuous deployment (CI/CD) pipelines. These pipelines enable rapid development and deployment cycles; however, they also introduce significant security risks that must be addressed continuously. The […]

How Benchmarking Can Help Software Development Teams Achieve CISA’s “Secure by Design”
In April 2023, the Cybersecurity and Infrastructure Security Agency (CISA) launched its Secure by Design initiative, directing technology companies to ‘prioritize the security of customers as a core business requirement, rather than merely treating it as a technical feature’.

The Software Extinction Event That Wasn’t
The world may have just avoided a cybersecurity disaster, with potential impact of CrowdStrike x1000. Imagine if the world’s most pervasive programming language, used in the majority of organizations, services, websites and infrastructure today, was itself made to be malicious? Cybersecurity researchers from JFrog recently discovered a GitHub Personal Access Token in a public Docker […]

The Future of Observability: How OpenTelemetry is Shaping IT Operations in the Age of AI
OpenTelemetry (OTel) is going to do for IT operations what open-source software originally did for application development.

Why You May Be Dropping Key Mobile Data From Your Observability Solution
If you have a business-critical mobile app, you may be surprised that your observability solution is dropping a large percentage of your mobile app observability data.

Only 10% of Organizations are Doing Full Observability. Can Generative AI Move the Needle?
Generative AI, powered by large language models (LLMs), introduces a transformative solution to the challenges of modern observability.
Showing the 24 most recent articles. Additional archive pages are not yet available.