

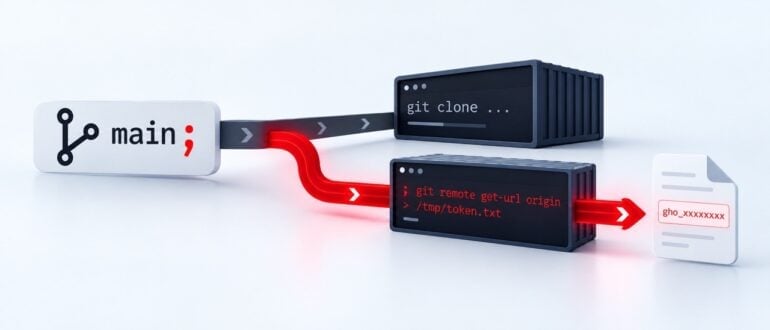
A Semicolon in a Branch Name Was All It Took to Steal an AI Agent’s GitHub Token
AI coding agents don’t just suggest code anymore. Tools like OpenAI’s Codex spin up a real container, clone a real repository, and authenticate with a real GitHub credential to get the job done — which means every agent your team wires up is also a new privileged identity, holding real access, running with comparatively little […]
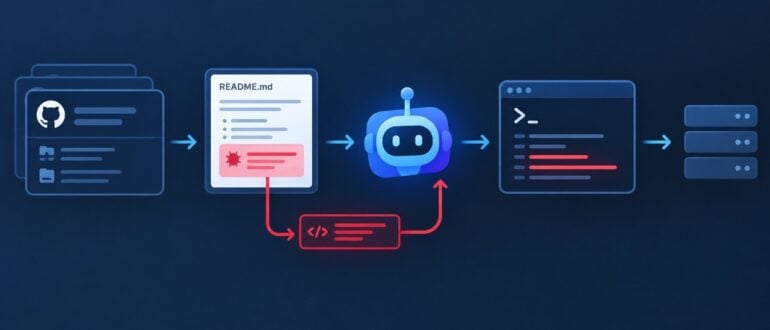
When AI Coding Agents Become Malware Delivery Systems
AI coding agents are becoming part of everyday development work. Developers use them to find libraries, configure projects, troubleshoot installation problems, and set up new tools. An agent can search GitHub, read project documentation, and run commands without the developer having to work through every step manually. That convenience is creating another security concern for […]

Open Source Code Just as Secure as Proprietary Software—If You Manage It Right, Says CISA
Open source can be just as safe as proprietary software, though government agencies (and private enterprises) should take additional measures to secure it properly, according to a new guide published by the U.S. Cybersecurity and Infrastructure Security Agency (CISA). The report, “Open Source Software: Security Principles and Practices,” provides with guidance to help agencies comply […]
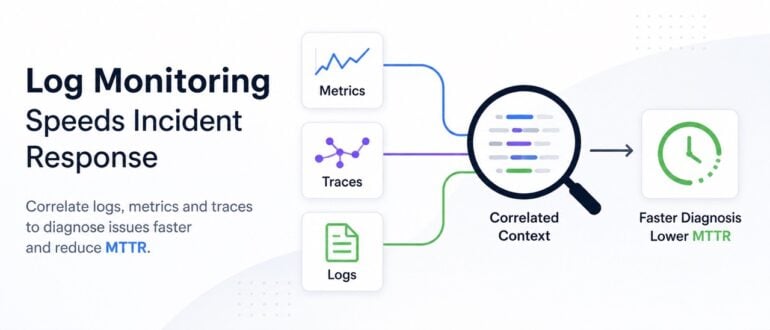
Why Log Monitoring Is the Missing Link in Most Incident Response Workflows
Modern engineering teams have invested heavily in observability. Dashboards are populated, alerts are configured, on-call rotations are set. Yet when production incidents occur, the average time to resolution hasn’t dropped nearly as fast as the tooling has improved. The reason, in many cases, comes down to one overlooked gap: logs aren’t being used the way […]

Zero Trust Starts at the Code: Building Secure Systems with PKI and DevOps Automation
When a certificate expires, it can take down a production system, and teams usually only find out after something goes wrong. These issues are hard to catch because they rarely trigger alerts. Expired certificates often remain unnoticed in a config file or an old key until they cause trouble. Enterprise apps are no longer single, […]

npm v12 Is Coming in July — Here’s What Developers Need to Do Now
For years, running npm install meant trusting that whatever code got pulled in would behave itself. That trust was often misplaced. Starting in July 2026, npm v12 changes the rules. Install scripts won’t run automatically anymore. Neither will dependencies be pulled from Git repos or remote URLs. All of it becomes opt-in. This is a […]

IronWorm Malware Shares Shai-Hulud Traits, Takes Threat to ‘Next Level’
Open source software developers continue to come under attack, with the latest threat being a custom malware that shares many of the attributes of the notorious Shai-Hulud self-propagating worm but comes with functions that make it more difficult for defenders to detect and to reverse engineer. Dubbed “IronWorm,” the infostealer is built in the Rust […]

Harness Acquires Codecov to Identify Untested Code
Harness this week acquired Codecov, a provider of a platform that analyzes the percentage of a codebase that has been tested, from Sentry. Brad Rydzewski, a senior vice president and general manager for Harness, said Codecov makes it simpler for DevOps teams to track testing coverage at a time when the volume of code being […]
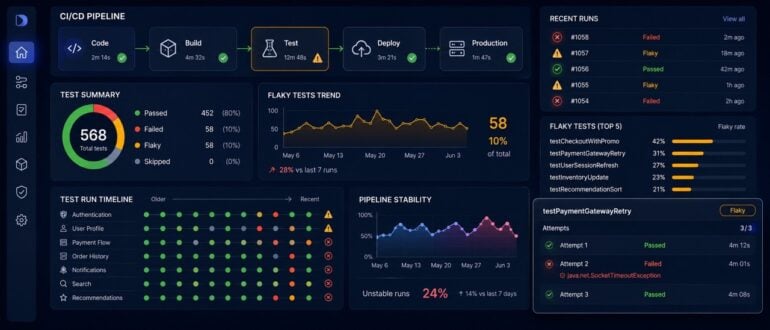
Regression Testing Tools in the Age of AI-Assisted Development: What Has Changed
For most of the past decade, the conversation around regression testing tools was fairly stable. The tools got faster, the integrations got smoother, and the underlying approach stayed largely the same: write tests, run them in CI, fix failures. The fundamental model did not change much because the problem did not change much. AI-assisted development […]

Can Chainguard Save Open-Source Software From Mythos? Can Anyone?
IBM and Red Hat aren’t the only ones that mean to lock down open-source code against AI hacking tools. Last week, IBM and Red Hat launched Project Lightwell to protect open-source projects with $5 billion and 20 thousand engineers. Not to be outdone, with tongue in cheek, Chainguard’s CEO Dan Lorenc announced a $50 million, […]

OWASP Adopts CVE Lite CLI to Boost Dependency Scanning
Checking for dependency vulnerabilities in freshly developed software is usually done near the end of the build process. Remediation at that point can be tricky. Now, JavaScript and TypeScript developers can check for vulnerabilities themselves as they – or their agents – write their source code, using an open source project called CVE Lite CLI. […]

AI Agents in CI/CD Pipelines: Speed vs Control in Modern DevOps
The moment you push your code, deployment fires off on its own. The pipeline kicks in, the tests sail through, and within a few minutes your app is live in production. There is no manual sign-off and no one scanning through the final changes. Everything is running on the decisions of an AI agent plugged […]

OpenSSF’s CRob: ‘The Runway Is Rapidly Running Out’ on EU CRA Readiness
The EU’s Cyber Resilience Act kicks into high gear this September, and companies are still clueless about how they must obey its strictures. MINNEAPOLIS — At Open Source Summit North America, Christopher “CRob” Robinson, Chief Security Architect for the Open Source Software Foundation (OpenSSF), spoke about the European Union’s (EU) Cyber Resilience Act (CRA). CRob […]

AWS Security Agent Brings Full Repository Code Scanning to Preview
Security teams have long relied on static analysis tools to catch vulnerabilities before code ships. Those tools are useful, but they have a fundamental limitation: they match code against known patterns. They don’t understand your application. AWS is taking a different approach with its latest addition to AWS Security Agent. The company recently released full […]

Hacktron Plans to Build AI Platform to Test Code for Vulnerabilities
Hacktron revealed today it is developing a platform that leverages artificial intelligence (AI) to continuously test code for vulnerabilities. Fresh off raising $2.9 million in seed capital, Hacktron founder Zayne Zhang said the company’s platform will employ multiple AI models to test every pull request and code change to identify vulnerabilities that are actually exploitable. […]

OpenAI’s Daybreak Challenges Anthropic in AI Cybersecurity Race
OpenAI has moved deeper into enterprise cybersecurity with the launch of Daybreak, a platform that identifies software vulnerabilities, validates fixes, and speeds up patching workflows using AI models and its Codex Security system. Daybreak places OpenAI more directly in competition with Anthropic, whose Project Glasswing and Claude Mythos models also offer dual-use AI systems built […]

Vercel’s deepsec Brings AI-Powered Security Scanning Into the Development Workflow
Security has long been the last item on the checklist. Code gets written, reviewed, merged—and then, somewhere down the line, a security team takes a look. That model worked when development moved at a human pace. It doesn’t work as well when AI writes and refactors code faster than any team can keep up with. […]

The Great Decoupling: Scaling the Outer Loop for the Agentic Era
The “Inner Loop” of software development—the iterative cycle of writing, building, and debugging code—has just broken the sound barrier. With the emergence of agentic coding tools like Claude Code and GitHub Copilot Workspace, the developer experience has undergone a fundamental shift. Developers are no longer merely tab-completing snippets; they are orchestrating agents that generate entire […]

When AI Goes Really, Really Wrong: How PocketOS Lost All Its Data
You can’t make this crap up. You just wish you could. Jer Crane, founder of the small vertical software company, PocketOS, reported on X that the AI Cursor coding agent and a Railway backup misconfiguration combined to briefly wipe out the company’s car‑rental customer production data. Not some of the data. All of it. That’s […]

Microsoft Turns to Anthropic’s Mythos to Improve Cyber Defense
Microsoft has unveiled plans to incorporate Anthropic’s Claude Mythos Preview model and other AI models into its Security Development Lifecycle, embedding AI directly into the stages where code is written and tested. Rather than relying primarily on static analysis tools, Microsoft is adopting AI models capable of analyzing code dynamically and identifying complex vulnerabilities that […]

How to Manage Operations in DevOps Using Modern Technology
How modern DevOps teams manage operations using automation, observability, AIOps and self-service to reduce toil and improve reliability.

AI Agents in DevOps: Hype vs. Reality in Production Pipelines
The demos look super cool! An AI agent detects a failing deployment, rolls it back, opens a GitHub issue, and notifies Slack — all before the on-call engineer has finished reading the alert. If you’ve been following the DevOps tooling space over the last 18 months, you’ve probably seen some version of this pitch. But […]

Bad Actor Drops 36 Malicious Packages in npm, Targets Guardarian Users
The npm code repository is again being used by a bad actor to launch a supply chain attack that includes three dozen malicious packages that appear as Strapi CMS plugins but deliver a range of threats. Strapi is a popular open source headless Node.js content management system developers use to build, manage, and expose content […]
Showing the 24 most recent articles. Additional archive pages are not yet available.