
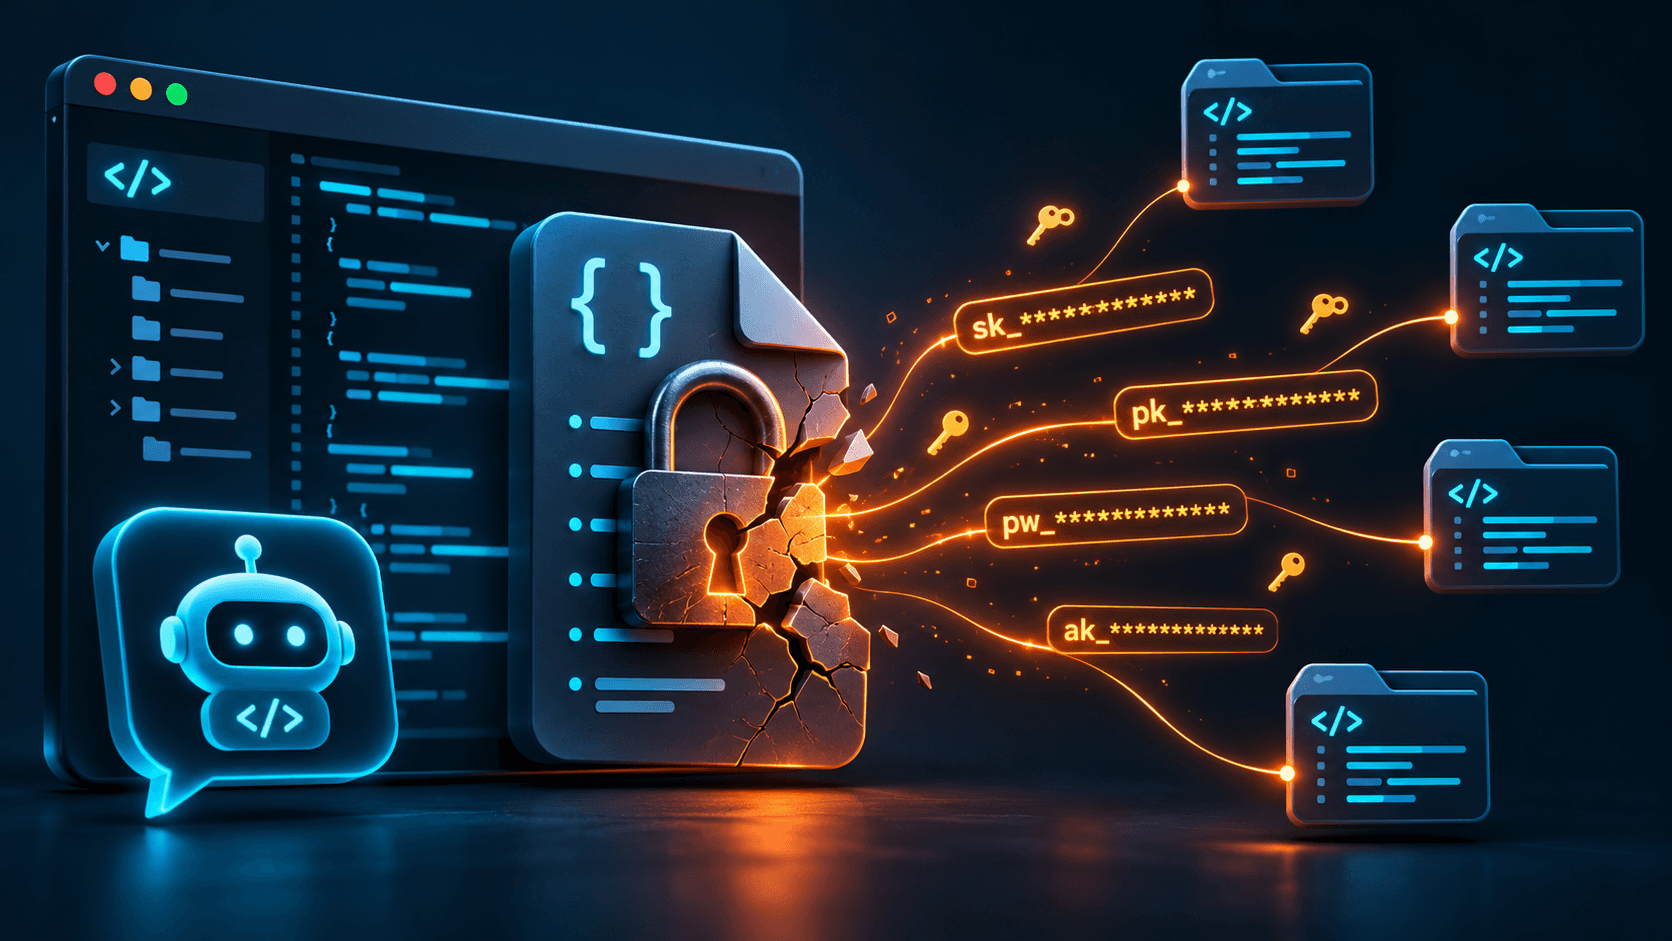
Anthropic’s Claude Code has exposed thousands of passwords, API keys and other sensitive credentials through a feature created to simplify developers’ daily work, according to research from software security firm Apiiro. The researchers identified 2,539 distinct secrets across 1,994 public GitHub repositories, including credentials that could provide access to cloud infrastructure and enterprise applications.
The findings highlight a major security issue for companies that use AI coding assistants: tools that automate software development can inadvertently expose the credentials needed to operate critical IT systems.
Apiiro found that 63 organizations were affected, including software vendors and companies managing sensitive customer information. One organization confirmed that a credential identified by the researchers had been active.
The larger concern here is that AI development tools are becoming part of enterprise software infrastructure without fitting established security controls. The findings demonstrate the need to treat AI coding assistants as another potential source of credential exposure, requiring the same oversight applied to developer endpoints and production systems.
How Claude Code Exposes Credentials
The security issue stems from Claude Code’s “Yes, and don’t ask again” permission option, which allows developers to authorize commands for repeated execution without requiring further approval.
Claude Code normally requests permission before executing many shell commands. When a developer grants ongoing approval, the tool can preserve the complete command in a configuration file called .claude/settings.local.json.
The problem is that commands sometimes contain passwords, authentication tokens or database connection details. These credentials can be stored as readable text alongside the approved command.
Although Claude Code attempts to exclude this configuration file from Git tracking, its protection relies on settings on the developer’s computer. The file can still enter a shared repository, potentially making its contents publicly accessible.
Expanding the investigation to include older Git commits, shared configuration files and saved AI agent conversations brought the total to 2,539 secrets across 1,994 repositories.
Among the exposed credentials were 379 database passwords, 122 Supabase service-role keys, 43 SSH logins and 23 AWS keys. Researchers also identified 42 authentication tokens associated with GitHub, GitLab and npm.
Among the affected organizations were a database vendor whose administrative cloud credentials were exposed, a company with a production payment-processing token and a medical-records application whose database credentials were accessible.
The discovery reveals the limited effectiveness of conventional credential-scanning tools. Of the 1,122 affected configuration files, Gitleaks detected 564 and TruffleHog identified 643. A total of 215 files escaped detection by both products. This gap reflects how security tools recognize credentials. Many scanners identify familiar API key formats but struggle with ordinary passwords embedded in shell commands.
The security risk goes beyond publicly accessible GitHub repositories. Credentials stored on developer laptops can also be collected by malware or inadvertently distributed through software packages and other shared files.
The exposure is not entirely new. Claude Code users reported plaintext credential storage in August 2025, months before Apiiro conducted its November 2026 investigation.
Anthropic has acknowledged the findings. Boris Cherny, head of Claude Code, indicated that Anthropic is considering built-in credential scanning and improvements to its automated permission system, although neither approach is guaranteed to eliminate the problem.
Apiiro recommends that organizations examine Claude Code configuration files, including deleted versions preserved in Git history, and replace potentially exposed credentials before removing the files. Security teams should also extend scanning to AI agent configuration folders and ensure developers use secret-management tools rather than inserting passwords directly into commands.

Frequently Asked Questions
1. How does Claude Code store sensitive credentials?
2. Why can a local configuration file become public?
3. Were the exposed credentials confirmed to work?

James Maguire is an award-winning technology journalist who has reported on emerging enterprise technology for more than 15 years. He began as editor of Datamation in 2006 before rising to become Editor-in-Chief of eWEEK, a technology publication founded in 1984, where he led a team of writers and analysts covering enterprise IT for 16 years, including a decade in senior editorial leadership. His coverage spans cloud computing, artificial intelligence, data analytics, cybersecurity and digital transformation, and he regularly interviews technology executives, analysts and vendors to track industry shifts. Maguire has won two ASBPE/AZBEE Awards of Excellence for feature writing on cloud computing and AI, and shared a 2013 PRSA Award for Excellence in Technology Journalism; Analytics Week has also named him one of its Top 200 Thought Leaders in Big Data. He holds a Master's degree in Interactive Communications with a focus on the internet. Beyond technology reporting, he is the author of two narrative nonfiction books, "Impresario: The Life and Times of Ed Sullivan" and "American Bee." Maguire now contributes technology journalism, editorial strategy, and produced/hosted video coverage across Techstrong Group properties.