
Blogs
Quick! Define DevSecOps: Let’s Call it Development Security
For a good long while, DevSecOps referred specifically to vendors like Veracode that did static application security scanning, dynamic application security scanning, software compo…
 a Futurum company
Tag
2 articles
Blogs
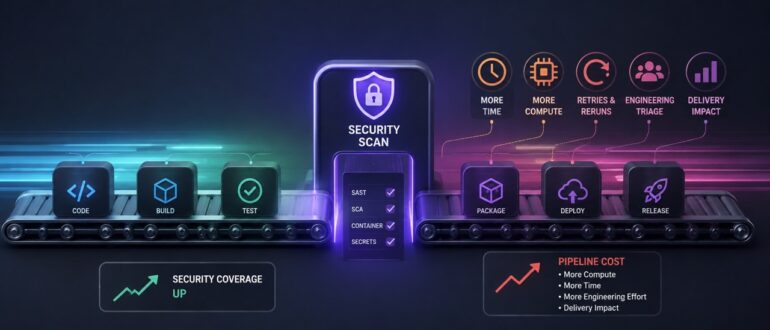
Security belongs in the software delivery pipeline. The harder question is where, how often and at what cost. Many pipeline teams eventually add security scanning to CI/CD, and relatively few go back afterward to measure what it a…
Showing 1–2 of 2
Blogs
For a good long while, DevSecOps referred specifically to vendors like Veracode that did static application security scanning, dynamic application security scanning, software compo…